General Data Protection Regulation (GDPR)
Review cloud controls against GDPR requirements with CloudAtlas. Identify configuration gaps and support your data protection and compliance planning.
General Data Protection Regulation Overview
Toughen your compliance standards with CloudAtlas security ready for GDPR enforcement. The General Data Protection Regulation (GDPR) establishes strict rules to protect and secure individuals' personal data across the European Union and global business partners.
Anomalies in personal identification and authorization can be controlled with rigorous adherence to GDPR principles. This covers the pseudonymization of entities involved in user identification to ensure data is rendered securely across web applications and cloud datacenters.
Active Directory authentication and single sign-on facilities modeled with CloudAtlas suite tools enhance on-premises and cloud applications for Governance & Regulatory Compliance (GRC) under GDPR.
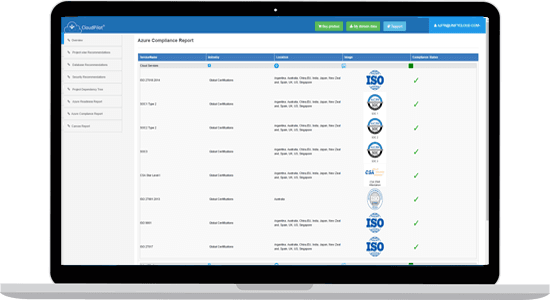
GDPR Readiness & Regulatory Compliance
End-to-end evaluation of personal data storage, cryptographic protection, and cross-border transfer controls across hybrid cloud architectures.
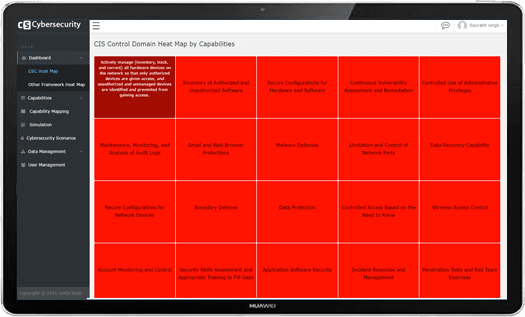
Role-Based Access & Cryptographic Security
Enforce least-privilege RBAC, data pseudonymization, and transparent audit logging for all personal information access.
Benefits of GDPR Implementation with CloudAtlas
Comprehensive data protection mechanisms that shield your enterprise from substantial regulatory penalties.
Unauthorized Access Notifications
Instant notifications and automated telemetry alerts whenever unauthorized or anomalous access attempts are detected.
Location-Specific Data Control
Geo-fenced cloud deployment recommendations to maintain sovereign control and regulatory compliance over cross-border data transfers.
GDPR-Composed Services
Cloud solutions and architecture patterns natively integrated and vetted against GDPR articles and GRC standards.
Analytical Intelligence & Encryption
Deep static code and infrastructure analysis ensuring end-to-end encryption of sensitive personally identifiable information (PII).
Transparent Service Architecture
Clear mapping of data controllers, data processors, and third-party SaaS integrations to maintain verifiable audit trails.
Authenticated CSP Solutions
Secure, verified integrations with hyperscaler Cloud Service Providers ensuring compliance boundaries remain unbroken.
Key Factors of the GDPR
Critical pillars every enterprise data architecture must satisfy.
Regulatory Imperatives
- Enhanced personal privacy rights and consent tracking for all European Union subjects.
- Increased affirmative duty for protecting customer, partner, and employee data across storage and transit.
- Mandatory 72-hour breach reporting protocols to supervisory authorities.
- Significant regulatory penalties for non-compliance (up to €20M or 4% of global annual turnover).
How CloudAtlas Supports GDPR Compliance
- Evaluates current on-premises and cloud codebases for unencrypted PII exposure.
- Verifies AD / Entra ID role-based access control and enforces least-privilege security.
- Provides automated executive compliance reports suitable for regulatory submissions.
Prepare Your Infrastructure for GDPR Governance
Ensure your data pipelines, storage accounts, and application databases are fully compliant with GDPR privacy standards.